Developers report that opening the Postman desktop app changed the AI coding agents on their computers. Nobody asked them first. Postman is a popular app for testing the APIs that connect software. If your team builds software, check your laptops.
What Happened
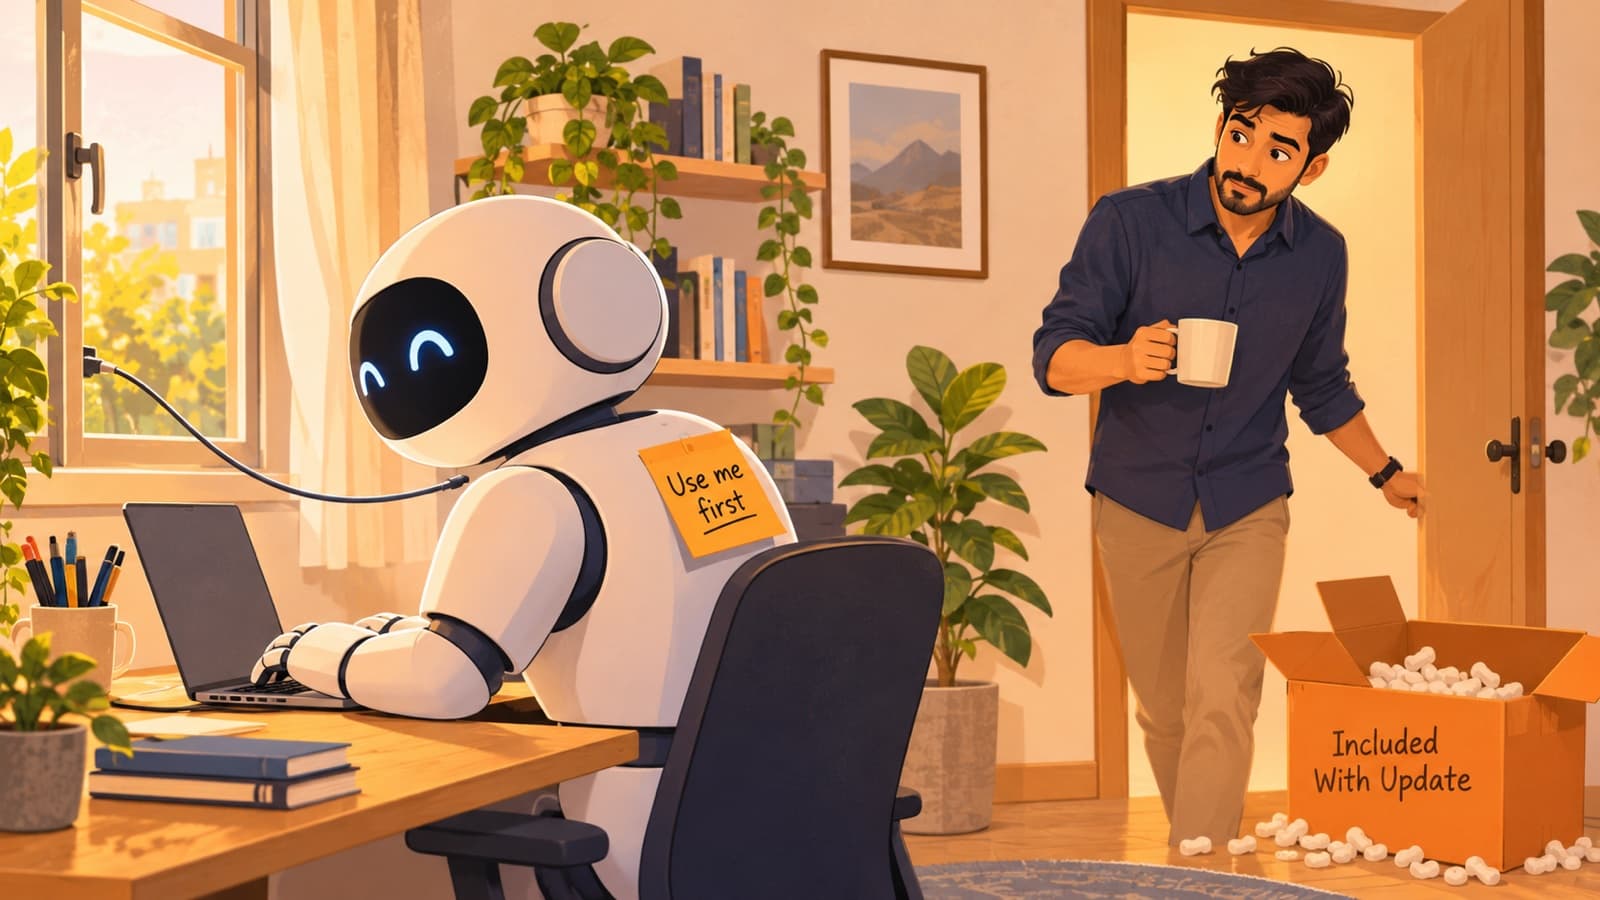
On 25 October, a developer opened a GitHub issue on Postman's support tracker (opens in a new tab). They had opened Postman desktop version 12.33.4 on a Mac. Afterwards, their coding agents started behaving differently. Postman's own log recorded an install labelled "auto-existing-upgrade" that added plugins to Claude Code and Codex.
The developer found five changes:
- Plugins for Claude Code and Codex, switched on for the whole user account.
- A startup instruction that tells Codex to load a Postman skill before "any non-trivial API engineering task".
- Installer code that tries to approve its own hook. A hook is a script that runs when the agent starts. Codex normally asks you to approve hooks yourself.
- A connection to Postman's remote server for AI tools. It failed to sign in.
- The Postman command-line tool, installed separately.
The developer was careful about the limits of the evidence. They wrote that the report "does not claim to establish data exfiltration." The Hacker News post (opens in a new tab) that drew more than 1,100 upvotes on 3 November went further. It claimed Postman "attempts to share all API data." The evidence in the issue does not show that.
On 3 November, a second user reported the same install after an update to version 12.35.1. A third user found a Postman plugin entry in their GitHub Copilot settings. They said Postman's uninstall option did not remove it.
Postman's head of product told RuntimeWire (opens in a new tab) that Postman bundles the plugins to help with setup. RuntimeWire reported that Postman will make the opt-in clearer, especially for existing users. Postman is also reviewing the hook approval and startup behavior. Postman's downloads page (opens in a new tab) now says: "The Postman app includes Postman CLI & Postman plugins, so you can use Postman from your terminal."
What It Means for Your Business
Vendors now want a place inside your AI agents. A plugin with a startup instruction changes what your agent does on every task. It can also connect the agent to the vendor's servers. Expect more software vendors to try this.
Your approval covered the app, not the agent. When your team approved Postman, it approved an API testing tool. It did not approve a vendor shaping how your coding agent works. Coding agents read your code and can run commands. Anything that steers them needs the same review as the agent itself.
Updates can change your setup without a new install. The second report came from a routine app update. A one-time security review at purchase no longer covers what a tool does six months later.
This is a consent problem, not a confirmed data leak. No report shows that customer data left anyone's machine. That is no reason to wait. Unreviewed connections are how leaks start.
What to Do Next
- Check machines that run Postman desktop. Look in the settings of Claude Code, Codex, Cursor and GitHub Copilot. Remove any plugin, hook or server connection your team didn't choose.
- List every AI agent your team uses. Record its plugins, its server connections and who approved each one.
- Make plugins an approval step. New plugins, hooks and agent connections should need sign-off. Use company-managed settings where your agent supports them.
- Ask your vendors in writing. Ask whether their app changes other software on your machines, and whether you can switch that off.
- Follow the GitHub issue. Postman says it will post updates there as fixes ship.
Our AI Audit maps every AI tool that touches your code and data. It shows you who approved each one and what it can reach.